
The RP2350 is actually a pretty secure chip, all things considered. It has secure boot, ARMv8’s TrustZone to split secure and non-secure execution, and you can permanently disable debug — the Pi Foundation even included glitch detection, meaning the traditional ‘zap the chip until it obeys’ technique is blocked. That’s why the [Ledger Donjon] security team went full Bond Villain and strapped everyone’s favourite fruit-flavoured microcontroller to a table with a slowly-approaching laser beam.
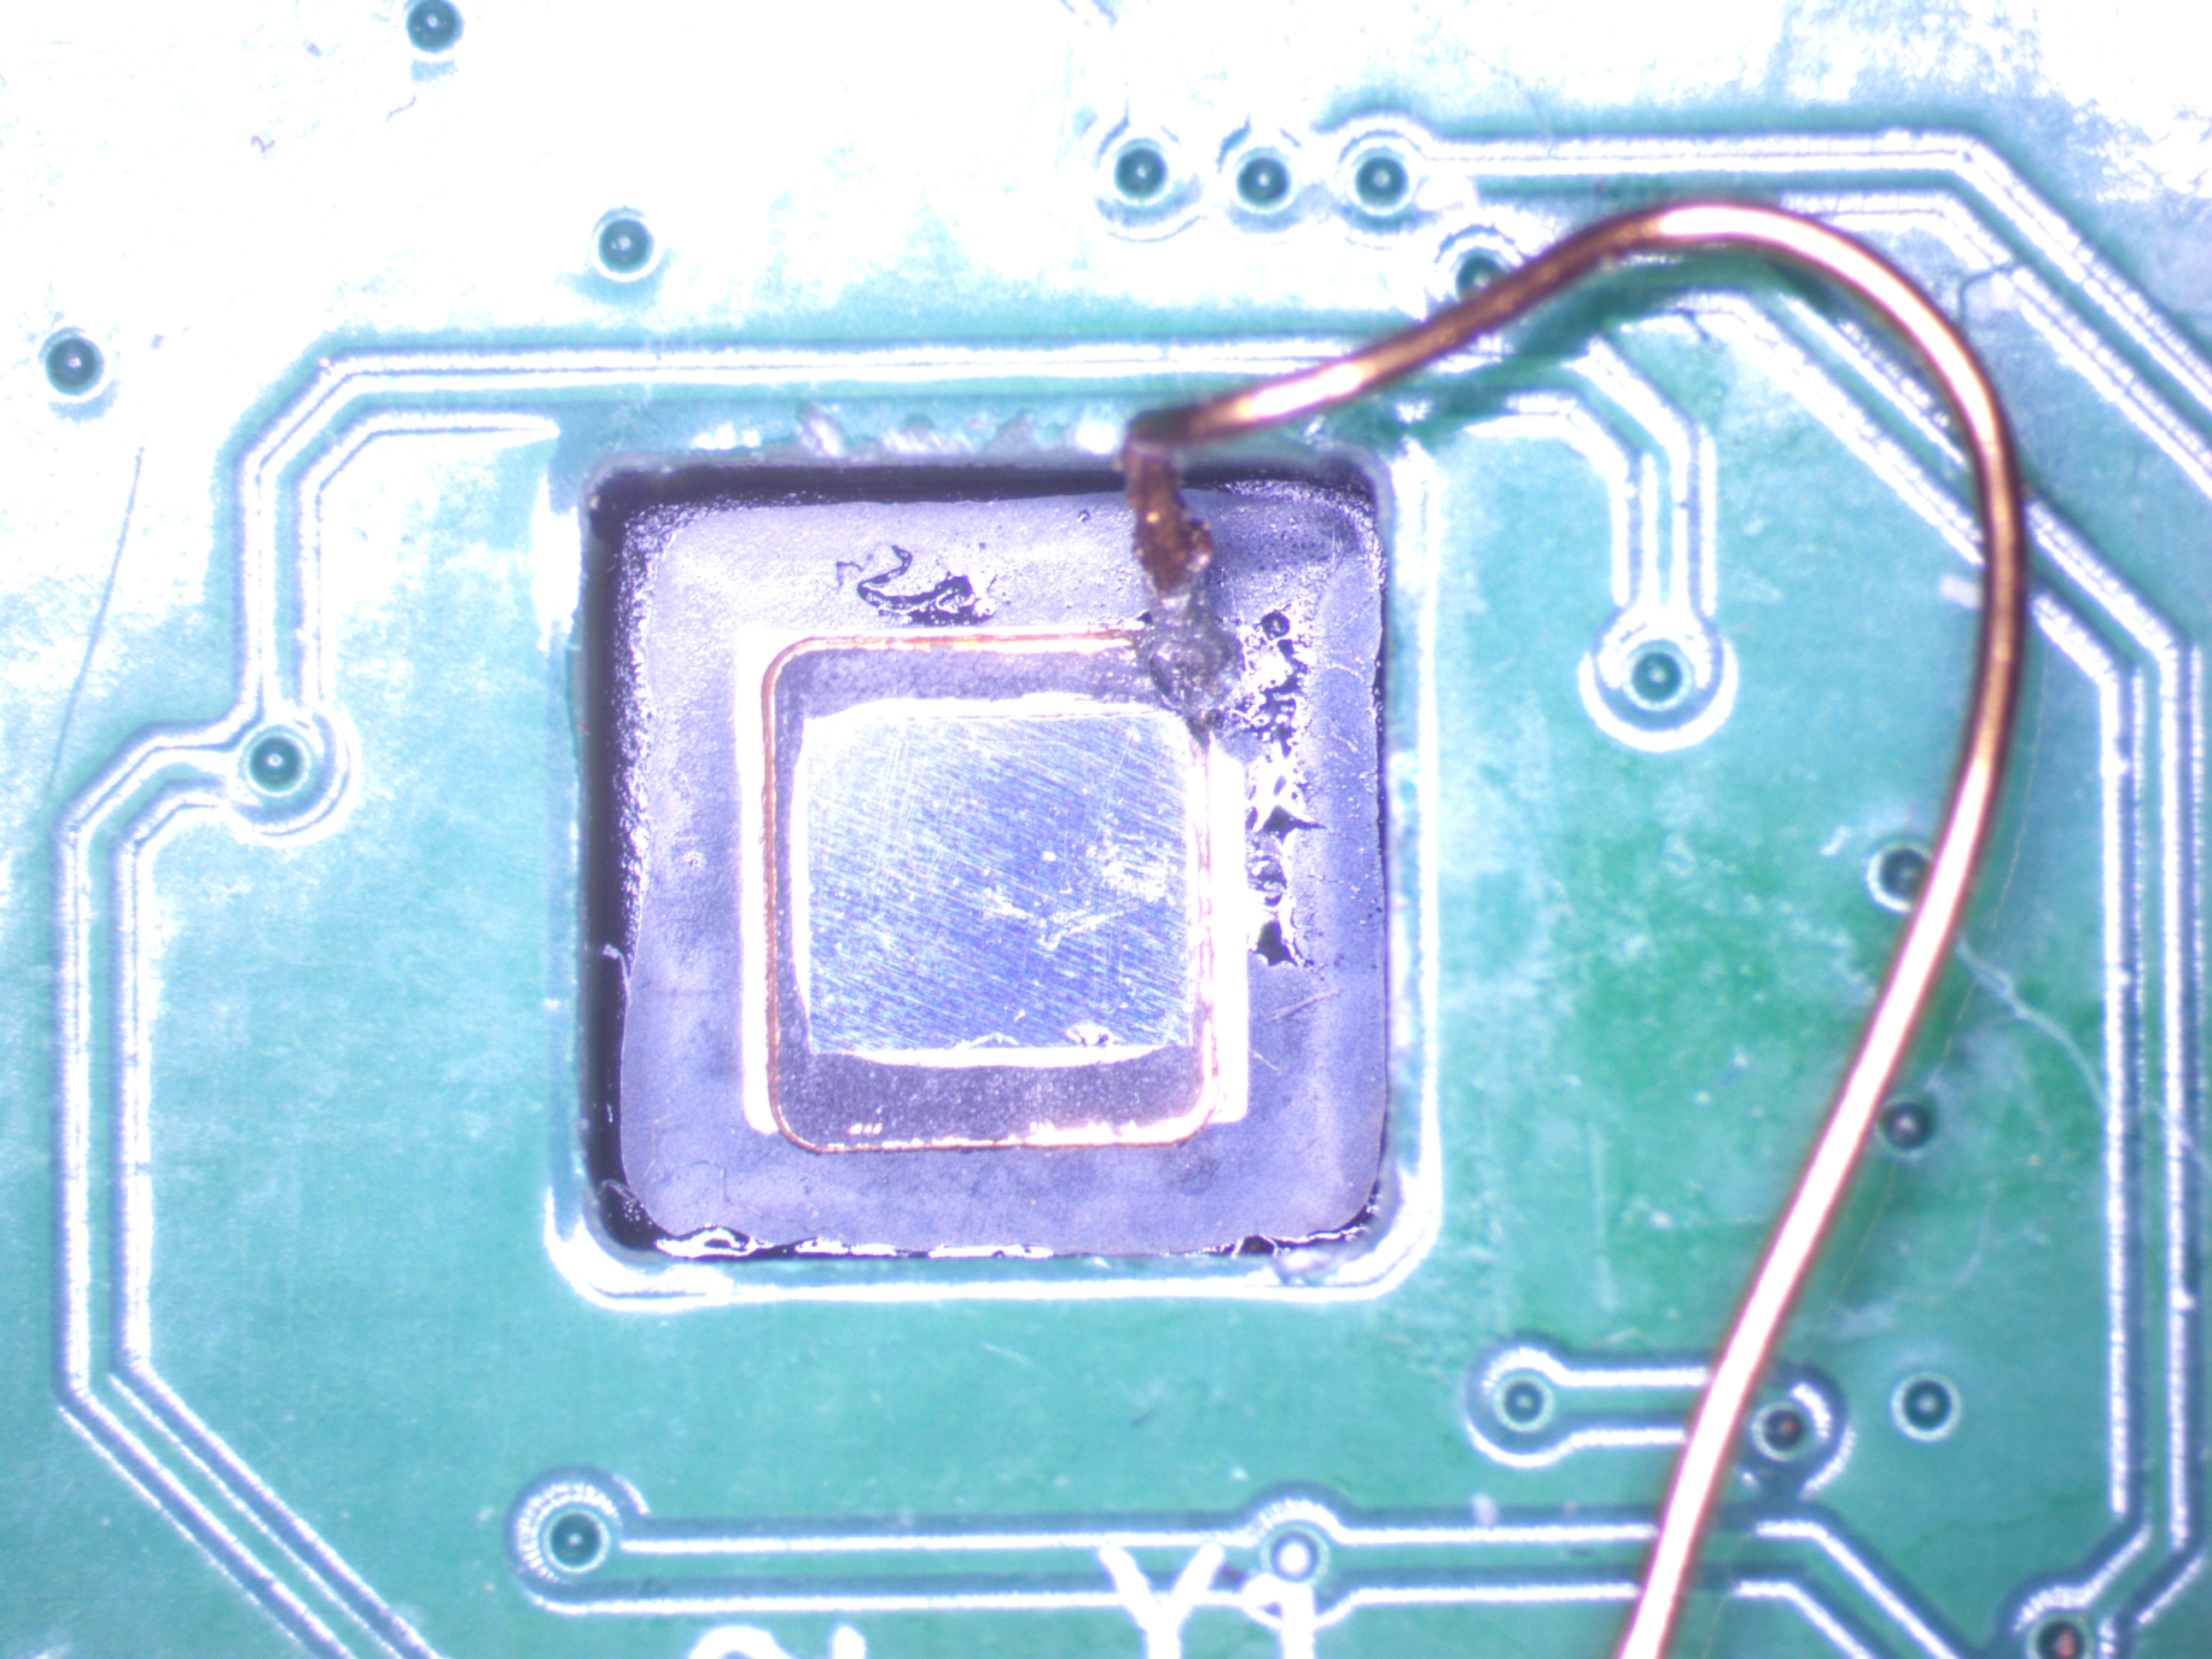
The bench setup to do all this is pretty impressive– and came with an impressive 250,000 USD price tag.Okay — movie clichés aside, the laser was in fact very carefully focused on target before they turned it on. That target was the register that enables the 2350’s debug features. Said register was located by decapsulating the chip and examining the die with photon-emission electron microscopy; the actual attack was carried out on a chip that had been decapped on the back side, with IR shining through the silicon wafer. There was probably more than a little trial-and-error to figure out exactly where on the die adjacent to the register to zap with the laser to flip those bits. But flip they did, restoring the debugger’s access to the secure execution zone. Then, after resetting the chip, [Ledger]’s team read the 128-bit secret the Pi Foundation hid in memory as part of the 2350 hacking challenge.
It’s long been accepted that once the black hats — or white hats, for that matter — have their hands on your hardware, they’re going to find a way in. The effort it takes to break into a simple microcontroller here is actually kind of impressive. We’ve talked about laser fault injection before; ironically, we’ve also featured Pi Pico-powered glitching attacks — the kind that this chip’s glitch detection thwarts.